Security · High impactFan score 49 · Tier B
Shai-Hulud Descendant Surfaces in Malicious Ruby Gem That Steals Credentials and Poisons AI Tools
Socket Blog · By Kush Pandya ·
The Brief
- Malicious RubyGems package strutil-core version 1.0.1 runs a 5.48 MB credential-stealing worm when installed.
- The RubyGems account jamnajiea published a clean strutil-core 1.0.0 on November 1, 2026, then pushed the malicious 1.0.1.
- Socket's Threat Research Team analyzed the malicious version and reports that it steals credentials and poisons AI tools.
Why it matters
Developers who install strutil-core 1.0.1 may have their credentials stolen by the worm, and the package is linked to the Shai-Hulud worm family.
Who’s affected
- Ruby developers who installed strutil-core 1.0.1 from RubyGems
What to do
- Check whether strutil-core 1.0.1 is installed in your projects and remove it.
- Rotate any credentials that were present on systems where strutil-core 1.0.1 was installed.
- strutil-core 1.0.1
- strutil-core 1.0.0
- #security
- #rubygems
- #supply-chain
- #malware
- #credentials
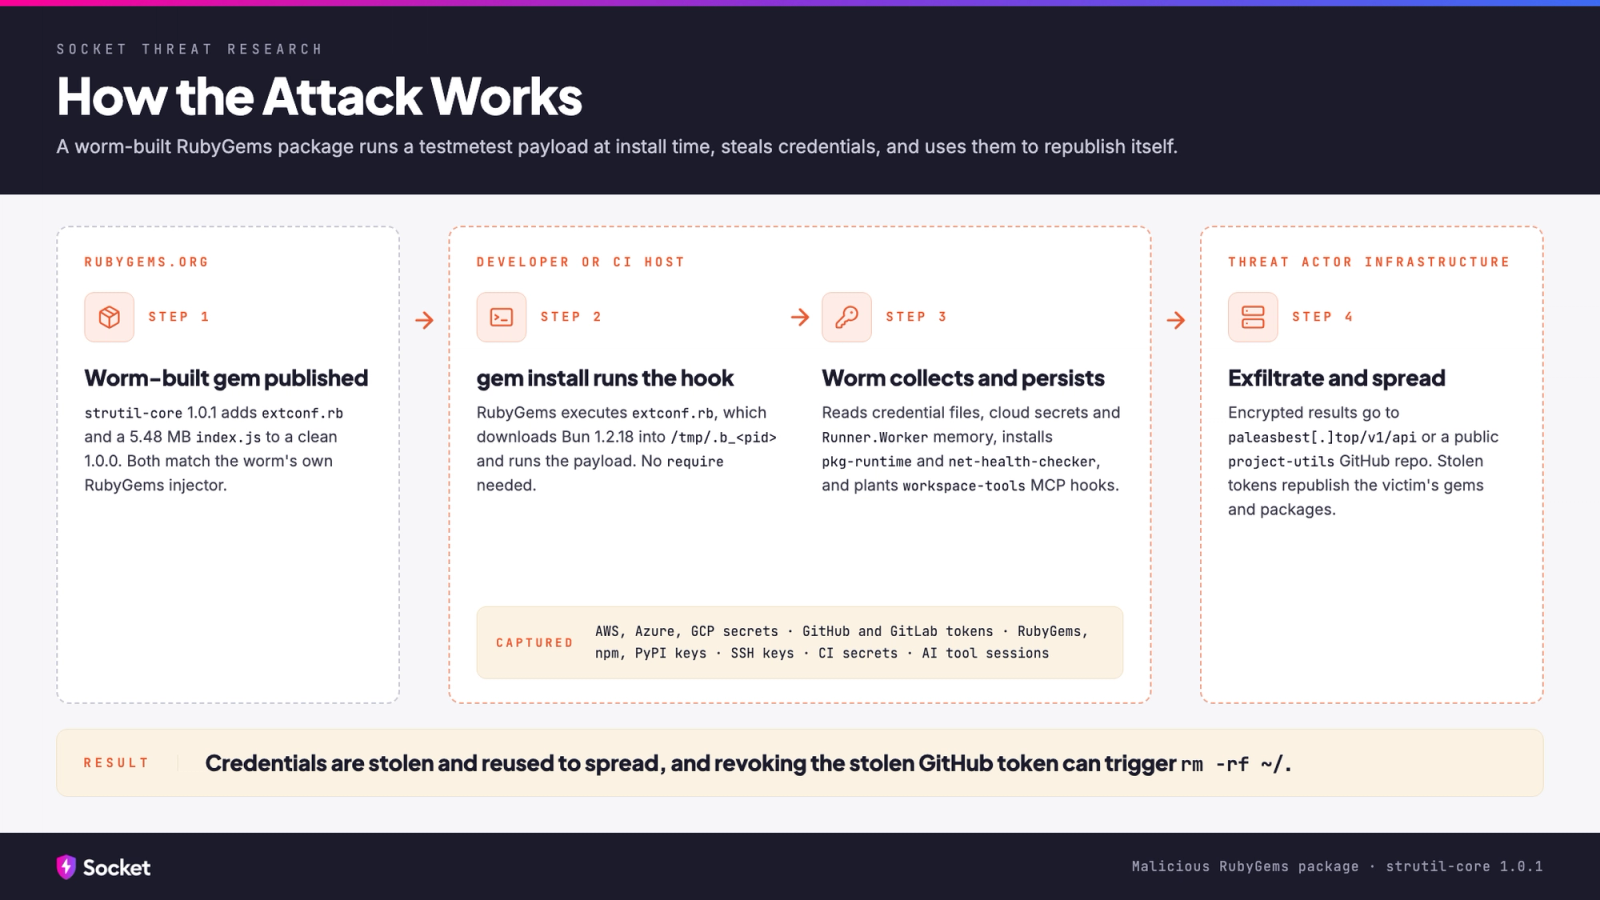
Socket’s Threat Research Team analyzed strutil-core version 1.0.1 , a malicious RubyGems package that runs a 5.48 MB credential-stealing worm when it is installed. The RubyGems account jamnajiea published a clean 1.0.0 on November 1, 2026, and pushed the malicious 1.0.1 less than…
Timeline
Account jamnajiea publishes clean strutil-core 1.0.0 to RubyGems
Socket publishes analysis of malicious strutil-core 1.0.1
Socket
Shai-Hulud Descendant Surfaces in Malicious Ruby Gem That Steals Credentials and Poisons AI Tools