The Morning Dev

Only the news worth knowing

‹
 
  • AAPL 344.17 ▼ 1.53%
  • MSFT 535.93 ▼ 3.58%
  • NVDA 181.60 ▼ 9.26%
  • GOOGL 282.57 ▼ 2.20%
  • AMZN 260.21 ▼ 2.19%
  • META 605.08 ▼ 3.96%
  • TSLA 343.69 ▼ 10.77%
  • AVGO 291.53 ▼ 10.43%
  • TSM 353.10 ▼ 10.78%
  • ORCL 115.16 ▼ 6.93%
  • AMD 404.40 ▼ 17.26%
  • NFLX 65.56 ▼ 1.25%
  • CRM 222.41 ▼ 2.07%
  • ADBE 246.44 ▼ 0.82%
  • INTC 52.25 ▼ 10.33%
  • IBM 247.11 ▼ 2.84%
  • PLTR 154.99 ▼ 9.73%
  • SNOW 269.54 ▼ 7.25%
  • NET 244.51 ▼ 8.28%
  • SAP 243.53 ▲ 1.45%

Policy

GitHub to Block pull_request_target Workflows by Default Starting December 2

Socket · By Sarah Gooding ·
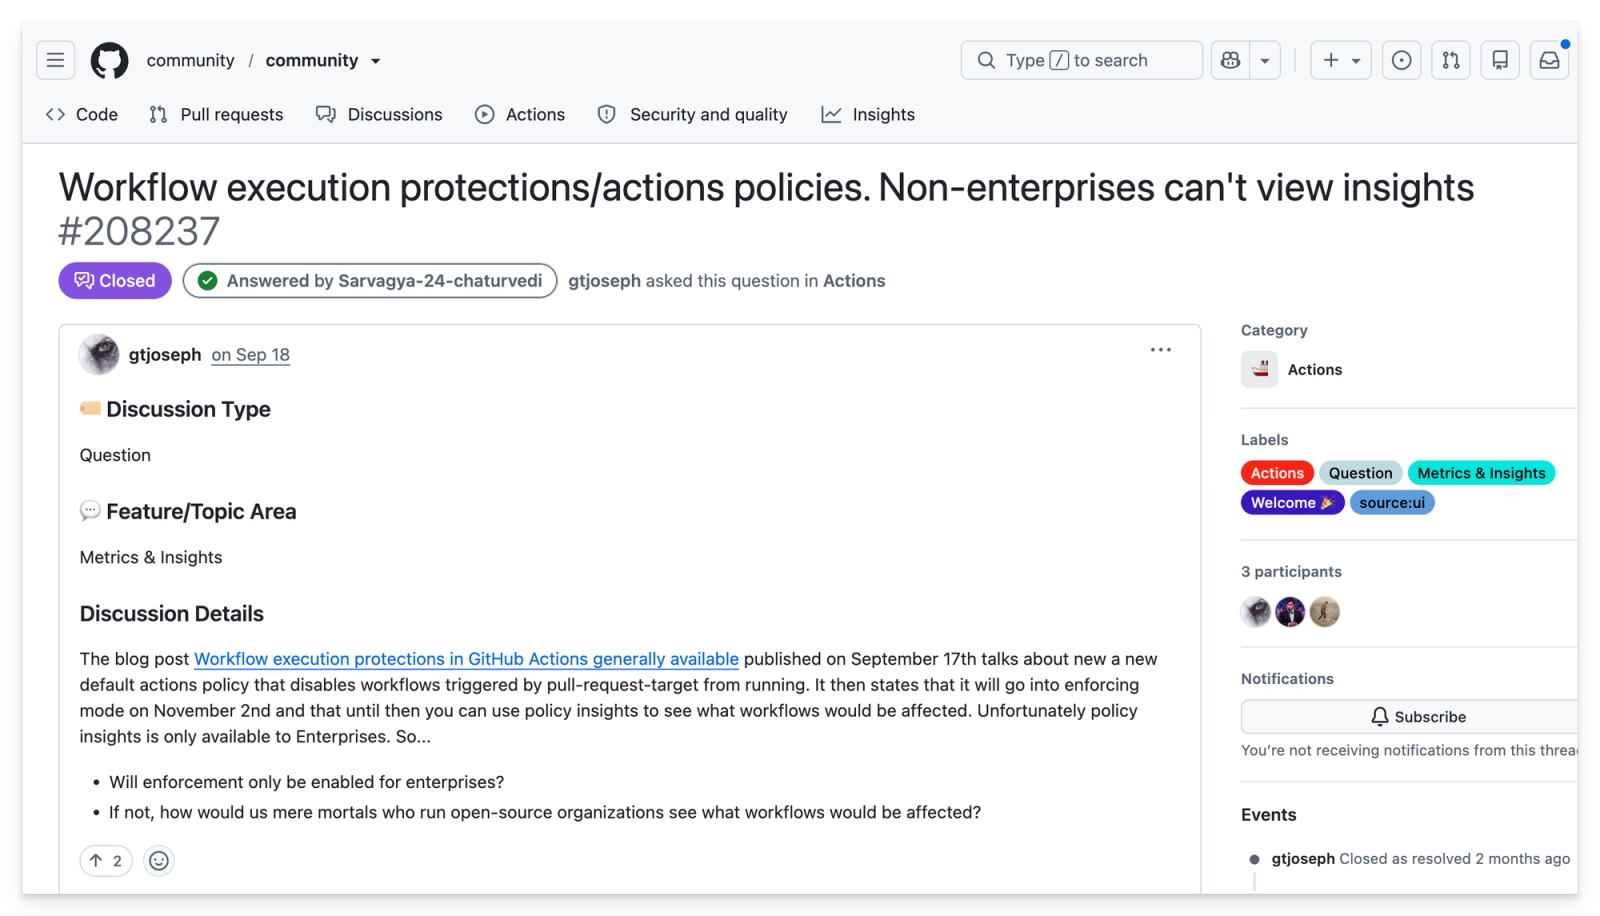
GitHub will begin blocking GitHub Actions workflows triggered by pull_request_target in public repositories on December 2, 2026, expanding its protections against a class of CI/CD vulnerabilities that has repeatedly enabled attackers to steal credentials and compromise open…

The Brief

  • GitHub will begin blocking GitHub Actions workflows triggered by pull_request_target in public repositories on December 2, 2026.
  • The change expands GitHub's existing protections against CI/CD vulnerabilities.
  • Sources say this vulnerability class has repeatedly let attackers steal credentials and compromise repositories.

Why it matters

Public repositories whose workflows rely on pull_request_target will stop running by default after the change, so their CI pipelines may break unless they are reviewed and adjusted.

Who’s affected

  • Maintainers of public GitHub repositories that use GitHub Actions
  • Teams with workflows triggered by pull_request_target

What to do

  1. Review workflows that use pull_request_target before December 2, 2026
  • #github-actions
  • #ci-cd
  • #github
  • #security
  • #supply-chain

Timeline

  1. Socket

    GitHub to Block pull_request_target Workflows by Default Starting December 2

  2. GitHub begins blocking pull_request_target workflows by default in public repositories
How do you feel about this?

0 Comments

    More in Security

    Security · High impact

    AI Agents Got Root on Linux via 948 Kernel Flaws in OpenAI Research

    An unreleased OpenAI cyber model found and exploited 948 distinct Linux kernel privilege escalation bugs for about $1.2 million. The post AI Agents Got Root on Linux via 948 Kernel Flaws in OpenAI Research appeared first on SecurityWeek .

    SecurityWeek · Eduard Kovacs · · 2 sources · 💬 353

    Security

    Want to Rent an Internet Address at the White House?

    Several staffers at the White House are using computers or mobile devices equipped with residential proxy services that render their internet address available for others to rent, security experts warned today. One of the proxy services is a Russian company whose founder’s web…

    Krebs on Security · BrianKrebs · · 2 sources · 💬 388